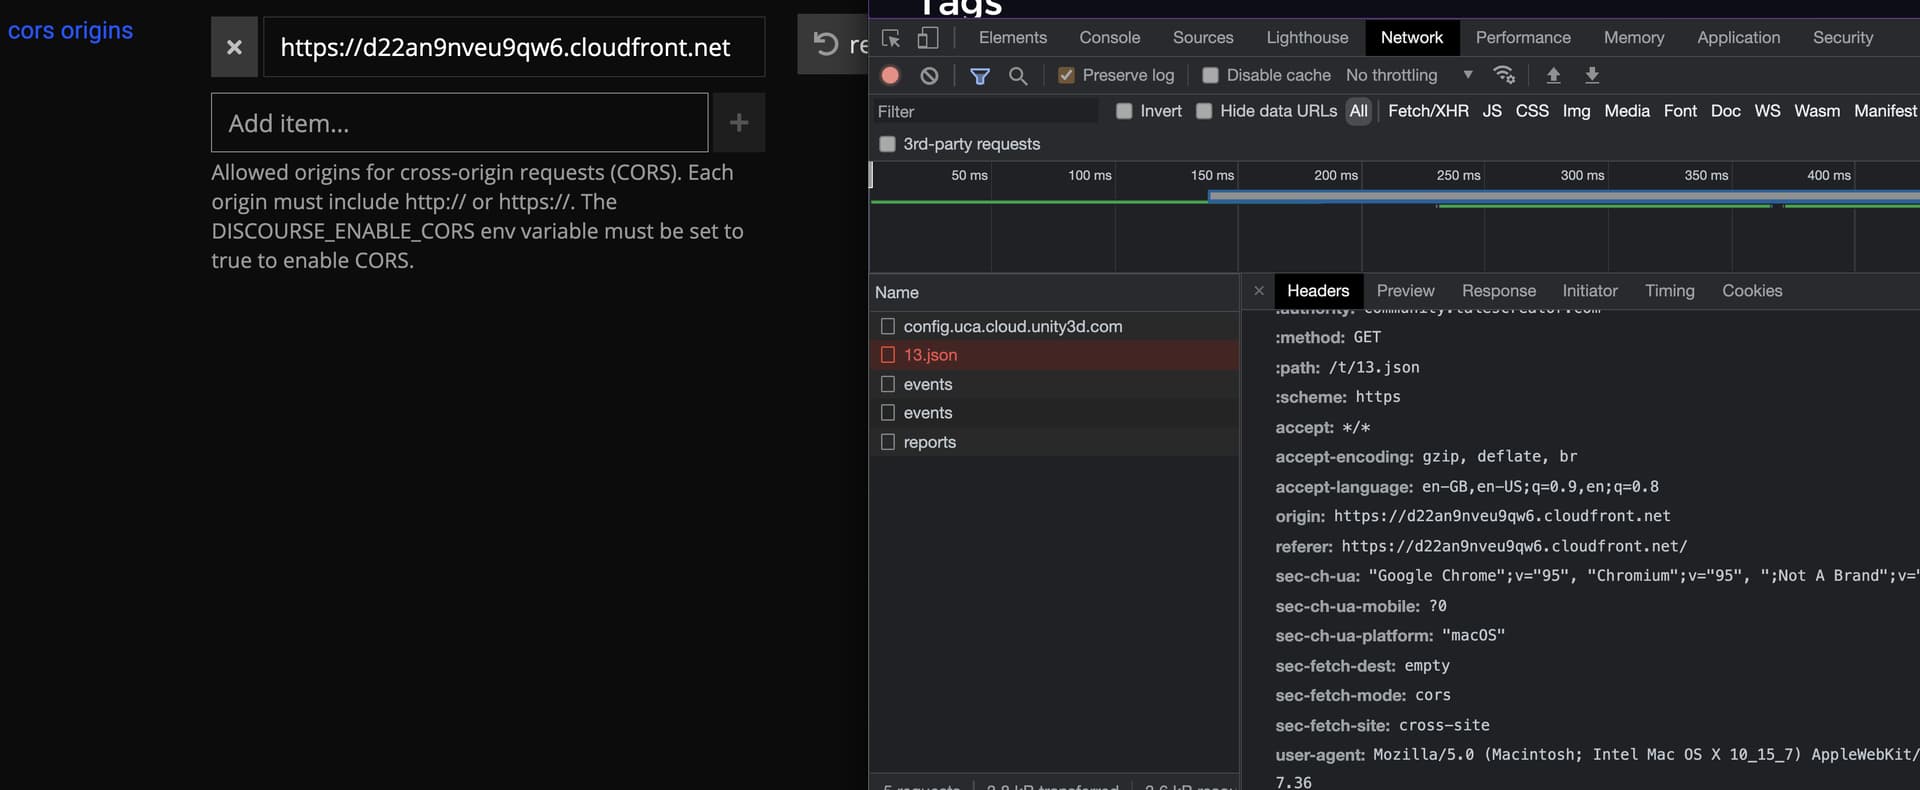
A user is experiencing issues with the ‘Access-Control-Allow-Origin’ header not being present despite setting DISCOURSE_ENABLE_CORS: true and DISCOURSE_CORS_ORIGIN: '*' in their app.yml file. They’re using a Unity-based iOS client and WebGL to interface with Discourse APIs, and the issue occurs when testing on browsers running WebGL.
IAmGav pointed out that CORS origins can be controlled in admin > settings > security, and only DISCOURSE_ENABLE_CORS is needed in the app.yml. However, xprmnts already attempted this and uploaded a screenshot showing the settings. xprmnts also mentioned that setting the origin in .yml vs. the admin UI should have the same effect.
Falco suggested trying a real domain instead of a wildcard, but xprmnts reported no success. They also attempted to debug and found that the OPTIONS call returns a 404 in the Nginx access logs, which precedes the error on the GET call.
Temporarily set ‘*’ to eliminate variables while testing. I have also attempted setting urls explicitly to no avail.
However, despite the above, we still get
Blockquote
No ‘Access-Control-Allow-Origin’ header is present on the requested resource.
Context: We have a unity based iOS client that interfaces with some discourse APIS and for testing we use WebGL. And we face this issue when testing on our browsers running WebGL specifically.
I am also observing from postman tests that all requests have a ‘strict-origin-when-cross-origin’ Referrer-Policy in the response headers.
I’m not sure we support the wildcard here. Can you try it with a real domain? We are using the cors settings in a couple sites with domains configured and it appears to work fine.
I attempted with a domain, no luck. Is there a way to confirm that the env vars are set correctly? (or that the app restart configured the cors without resending requests, just trying to think of ways to debug).
I think this is the part of code that handles the cors settings, just in case it is useful.